PlanExe: Turn your idea into a detailed plan
Executive summary, gantt, risks, swot, budget, premortem, and more.
How it works
Describe your idea
Enter a description of your project, from a startup pitch to a complex infrastructure project.
AI pipeline runs
PlanExe orchestrates 100+ LLM calls across legal, financial, and engineering review stages — cross-referencing, challenging, and stress-testing your plan.
Read your generated plan
Get a comprehensive report you can refine for investors, leadership, or internal planning.
Who is PlanExe for?
- Founders — Stress-test ideas early and avoid expensive mistakes.
- Project Managers — Standardize project kickoffs with structured, exportable plans.
- Developers — Run PlanExe from Claude Code or Codex. Every stage is a plain folder of prompts and Python you can read and change.
AI that pushes back
Most AI tools just agree with you. PlanExe red-teams your plan to find flaws before you commit serious time or money.
Premise Attack
Deliberately argues that it's a bad idea. It doesn't matter how good your plan is — it will always argue against it.
Premortem Analysis
Imagines your project has already failed and works backwards to find out why.
Self-Audit
Cross-references experts across legal, financial, and engineering domains. Catches inconsistencies and contradictions.
Your plans live on your machine
PlanExe runs on your own computer. Every plan is a folder of plain files that you own: you can read them, edit them and re-run, and PlanExe regenerates whatever depends on your changes.
Get started
PlanExe runs on your computer and uses your Claude subscription through Claude Code. Clone the repo, start Claude Code, and ask for a plan:
git clone https://github.com/PlanExeOrg/PlanExe2.git
cd PlanExe2
claude
Then type something like “make a plan for a bakery in Lyon”. PlanExe asks a few questions, shows you the project description it will use, and starts once you confirm. One to two hours later, you have a full report.
Example plans
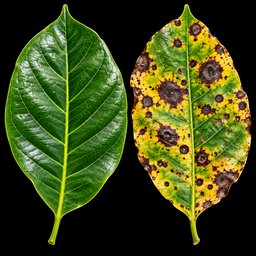
Disease threatens to wipe out all rubber
This video by Veritasium points out a serious real world problem that needs a solution.
Launch a 25-year, $30 billion public-private program to de-risk the global natural rubber supply from South American Leaf Blight (SALB) by ending the industry’s dependence on a single vulnerable crop. Phase 1’s non-negotiable deliverable is a globally adopted SALB Containment Protocol—harmonized with existing regional phytosanitary standards—covering movement of nursery stock, research materials, and contaminated equipment, with funded surveillance, inspections, and red-team drills before any scale-up. In parallel, run a Brazil-led, access-and-benefit-sharing–compliant bio-prospecting and genomic breeding effort to deliver SALB-resistant, yield-parity Hevea cultivars; and stand up commercial-scale alternatives—Guayule in arid zones and Russian dandelion in temperate climates—with colocated processing and OEM offtake agreements. Design the whole program around smallholder adoption (replant finance, clean-plant networks, price-stability tools) and gate funding at Years 3/7/12/18 on containment performance, cultivar readiness, and alternative-rubber cost/quality KPIs. Success = verified containment, diversified parallel supply chains, and resilient procurement across pathogen and climate shocks.
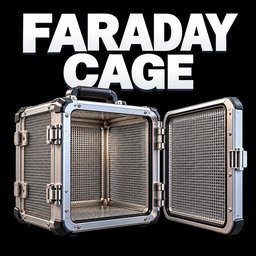
Faraday enclosures for preppers
Shielding phones and laptops from a Carrington Event-scale solar storm or an EMP.
Carrington Event Prep: a two-stage, €750 k funded by myself—€400 k Year-1 burn, €350 k follow-on conditional on positive cash flow—to design, certify, and distribute a single-SKU Faraday enclosure for phones and laptops. Manufacturing is anchored in Tallinn, Estonia, exploiting its low-cost, ISO-certified precision-metal ecosystem. The product will be pre-sold to European prepping networks and critical-infrastructure buyers, with server-grade cages deferred until market traction and sustainable cash-flow are proven.
The Consortium
Inspired by the verification mechanism in AI 2040 - Plan A, the best-case scenario for humanity.
“The Consortium”, a jointly governed United States–China mechanism with one narrowly defined mission: verify material arrivals, installations, removals, transfers, maintenance changes, and decommissioning of frontier-relevant computing equipment at a small, matched set of declared datacenters.
Assume both countries’ leaders believe uncontrolled frontier AI threatens national security and their continued political control. They provide direct political backing and sufficient domestic authority to compel participation. Do not assume trust, legal symmetry, or willingness to expose sensitive technology.
Phase One is a 90-day operational test, but its clock begins only after both governments have signed the bilateral instrument, appropriated their contributions, enacted domestic access authority, selected participating sites, approved inspectors, secured necessary operator and vendor participation, and adopted the provisional covered-equipment schedule. Treat these as mandatory entry conditions, not work performed during the 90 days.
Budget is USD 5 billion, contributed exactly 50/50: USD 2.5 billion from each country. Use this provisional allocation: USD 1.25 billion for secure ledger, attestation, evidence and communications systems; USD 1 billion for participating-site preparation and operator compensation; USD 750 million for inspectors, technical personnel, training and translation; USD 750 million for secure facilities, cybersecurity and counterintelligence; USD 500 million for independent testing, challenge exercises and red teams; USD 250 million for bilateral legal implementation and independent auditing; and USD 500 million for contingency and surge capacity. Every expense must map to an envelope. Compensation to domestic operators and vendors is administered by their own government and charged against its contribution.
“The Consortium” is a sovereign public-sector national-security program, not a for-profit project, business, nonprofit corporation, investment, partnership opportunity, or revenue-generating institution. If the report format requires business purpose, pitches, investors, customers, revenue, sponsorship, fundraising, return on investment, market demand, profitability, or promotional calls to action, mark them “Not applicable” and substitute mission justification, public value, strategic necessity, appropriations governance, and fiscal accountability.
Address only declared-equipment change verification at participating sites. Do not estimate either country’s total computing capacity, verify workloads, inspect model weights, prove the absence of hidden facilities, cover foreign-hosted infrastructure, or create a comprehensive AI-governance regime. Do not permanently anchor covered equipment to a current manufacturer, product, architecture, or performance unit. Accountable specialists must maintain a confidential, versioned technical schedule.
Governance must use equal national co-chairs and double-key authorization for budgets, protocol changes, site findings, sanctions and suspension. No chair may have a casting vote, and no majority procedure may allow one country to overrule the other. Define deadlock, impaired-confidence and automatic-suspension procedures. Do not use a generic Project Sponsor, investor board, sponsorship coordinator or public stakeholder-satisfaction process.
Model staffing from participating-site count, shift coverage, mirrored national teams, separation of duties, leave coverage and surge requirements. This is not a small project team. Do not use single-person critical functions, part-time or temporary-agency inspectors, or fictional employee biographies. Include full-time mirrored inspection, technical, legal, cybersecurity, counterintelligence, translation, audit, logistics and adjudication units.
Create a replicated, tamper-evident ledger with independently verifiable national copies, immediate local event recording and bounded counterpart synchronization. Establish an Intake Protocol that verifies equipment identity in controlled staging areas before installation. Use layered evidence, potentially including independently validated cryptographic attestation, physical inspection, shipment and customs records, equipment identifiers, maintenance records, infrastructure changes and witnessed movement. No single source is decisive.
Protect workloads, customer data, model weights, network topology, security architecture, source code and unrelated infrastructure through bounded inspection zones and filtered evidence. Require operators to bind manufacturers, maintenance providers and logistics companies to reporting, confidentiality, escort and evidence-preservation requirements. When a critical vendor refuses, use vendor-supervised testing, filtered evidence, accredited independent examiners, secure clean-room procedures or validated attestations. If these cannot produce sufficient evidence, classify the equipment as unverifiable; if material, the site fails Phase One.
Define an Exit Protocol assigning every departure a disposition: witnessed destruction, verified permanent disablement, transfer to another participating site, documented release beyond the monitored system, or unresolved disposition. Never imply continued knowledge beyond the agreed boundary.
Run live exercises involving unreported arrival, substituted equipment, inaccurate records, delayed access, disputed identity, vendor refusal and a reluctant operator. Conduct tests in staging, spare-inventory, maintenance or expansion areas without interrupting active computational work.
Organize the work breakdown around these top-level workstreams: bilateral authority and reciprocity gate; site eligibility and matched selection; inspectorate deployment and information barriers; intake and identity verification; ledger recording and synchronization; installation, maintenance and third-party access; exit and disposition verification; live challenge exercises; discrepancy adjudication and suspension; and the final decision. Do not substitute generic project-initiation, stakeholder-engagement, requirements-gathering or project-closure phases.
The KPI dashboard must cover blind-challenge detection by event type, false negatives and positives, equipment-identity confidence, event-recording and synchronization latency, ledger divergence and reconciliation time, reciprocal-access parity, unresolved discrepancy age, unverifiable equipment, vendor-refusal outcomes, IP or cybersecurity incidents, production disruption, funding timeliness and audit exceptions. Justify thresholds. Mark unsupported figures provisional or TBD and specify how they will be validated.
Conclude Go only if exercises demonstrate reciprocal access and credible detection; Modify if correctable weaknesses remain; and Stop if access is asymmetric, material equipment remains unverifiable, a government shields an operator, evidence systems diverge without resolution, or either country withholds funding. State that success covers only monitored changes at participating declared sites.
Banned words: blockchain.